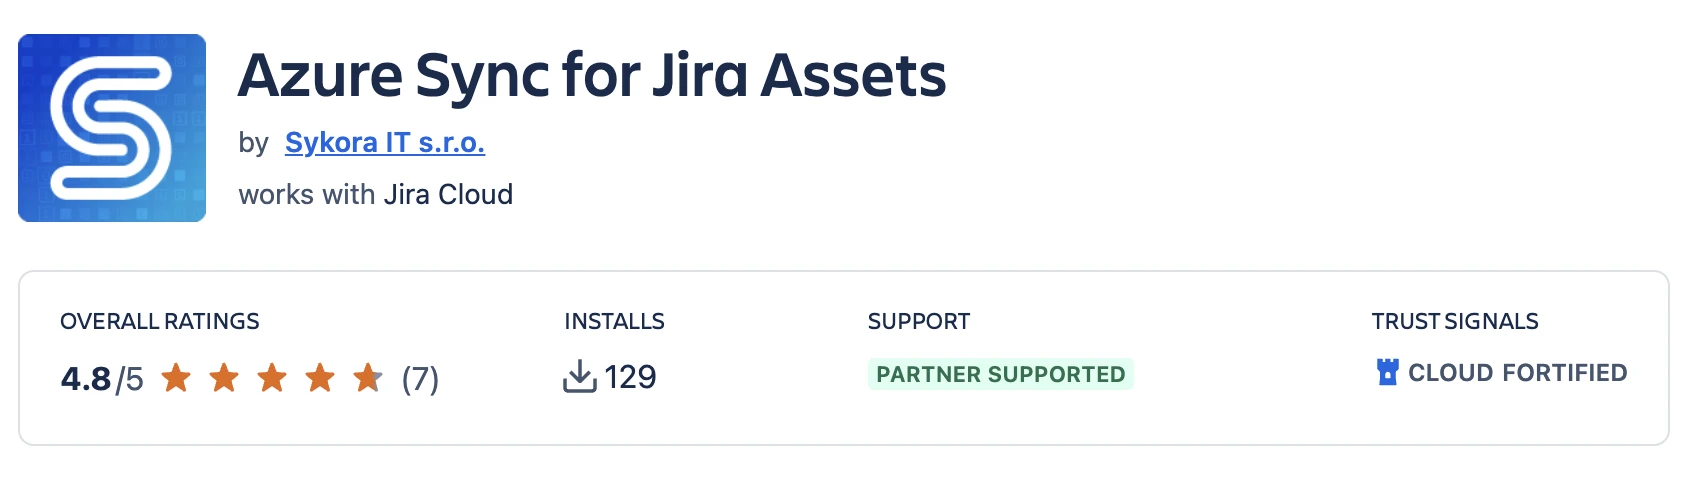
When evaluating an app on the Atlassian Marketplace, customers can compare its functionality, pricing, reviews and number of installations. They may also see different trust badges and security indicators.
These badges are more than visual labels. They help administrators, security teams and procurement departments understand how an app is built, where its data is processed and whether the vendor follows additional security, reliability and support practices.
The badge is particularly valuable to organizations with strict data residency and data processing requirements. However, it is not applicable to every app architecture. For example, an integration whose core purpose is to communicate with an external business system may need external connections by design.
That does not automatically make the app less secure. It simply means that Runs on Atlassian describes a specific architectural model rather than serving as a universal security rating. (Runs on Atlassian)
Has the vendor established the security, operational and support processes expected from an enterprise application provider?
Atlassian states that the program is designed to make it easier for enterprise customers to evaluate Marketplace apps and to give eligible apps greater visibility among customers with business-critical requirements. (Cloud Fortified Apps Program)
What Cloud Fortified means for Marketplace customers
For an Atlassian administrator, procurement team or information security department, Cloud Fortified provides a valuable initial trust signal.
It indicates that the app vendor has gone beyond the baseline security requirements applicable to Marketplace cloud apps and has established processes for:
publishing structured privacy and security information,
exposing the app to independent security researchers,
evaluating and remediating reported vulnerabilities,
monitoring reliability and responding to production incidents, and
supporting customers within a defined response time.
However, Cloud Fortified is not a guarantee that an app is free of vulnerabilities. It is also not a regulatory certification and does not remove the customer’s responsibility to assess whether an app is suitable for its environment.
Before installing any Marketplace app, customers should still review:
requested app permissions,
data accessed and processed by the app,
data storage and data residency,
external data transfers,
retention and deletion rules,
subprocessors and external services,
vulnerability and incident management,
support contacts and response commitments, and
the vendor’s privacy and security documentation.
The badge is a strong starting point for due diligence, but the information behind the badge remains just as important as the badge itself.
What Cloud Fortified requires from developers
From a developer’s perspective, Cloud Fortified is not simply an application form or a one-time technical review.
The vendor needs to introduce and maintain processes around security documentation, vulnerability management, application monitoring, incident response, production readiness and enterprise support.
The security requirements include:
Completing all relevant questions in the app’s Marketplace Privacy & Security tab.
Enrolling the app in the Atlassian Marketplace Security Bug Bounty Program.
Giving external researchers sufficient access and time to test the app.
Reviewing submitted findings within the required time.
Remediating critical and high-severity vulnerabilities in accordance with Atlassian’s security timelines.
The reliability requirements add further work. Developers must assess the app’s scalability and performance, establish a documented service restoration plan, implement incident management processes and test core app functionality against Atlassian’s pre-release environment.
Cloud Fortified vendors must also provide a support contact and respond to critical requests within 24 hours, five working days per week in the partner’s local time zone. (Cloud Fortified requirements)
In practice, the reliability and support requirements can be just as demanding as security: incident response, SLO monitoring, and enterprise support commitments require ongoing operational ownership, not just a security workflow.
How the Bugcrowd security program works
Participation in the Atlassian Marketplace Security Bug Bounty Program is one of the central Cloud Fortified requirements.
The program is operated through Bugcrowd, a platform that connects organizations with independent security researchers. Unlike an internal test performed by the development team, the bug bounty exposes the application to specialists who may approach its permissions, APIs, user roles and data flows in unexpected ways.
The typical process is:
The Marketplace Partner defines which applications and environments are in scope.
The partner prepares instructions, test accounts and setup information for researchers.
Bugcrowd invites researchers to the program.
Researchers test the app within the defined scope.
Potential vulnerabilities are submitted through Bugcrowd with reproduction details.
Bugcrowd’s Application Security Engineering team checks whether a report is reproducible and within scope.
A corresponding ticket is opened in Atlassian Marketplace Security (AMS).
The app developer accepts or rejects the triaged report within two weeks.
If accepted, the developer implements a fix, tests the remediation, and rewards the researcher based on severity.
To be shown as participating in the program on the Marketplace, an eligible app must currently be in scope for at least four weeks and at least 100 security researchers must have been invited. Going further, Atlassian now requires Marketplace bug bounty programs to be public, or actively scheduled to go public, by 30 June 2026. Programs preparing for public launch typically need at least 250 invited researchers for at least two weeks, along with other readiness checks such as a funded reward pool and a manageable queue of open critical findings.
Partners must accept or reject reports within two weeks after Bugcrowd has triaged them. Critical and high-severity findings must be remediated within Atlassian’s applicable security timelines. (Marketplace Security Bug Bounty Program)
What does the Bugcrowd program cost?
Atlassian covers the Bugcrowd platform costs for Marketplace Partners. The app developer does not pay for access to the Bugcrowd platform and its services.
The Marketplace Partner is responsible for the rewards paid to researchers for valid findings.
At the time of writing, Atlassian specifies the following minimum payout structure:
|
P1 – Critical | USD 1,500 |
P2 – High | USD 900 |
P3 – Medium | USD 300 |
P4 – Low | USD 100 |
P5 – No appreciable security impact | USD 0 |
Partners are requested to fund an initial Bugcrowd reward pool of at least USD 5,000. This is a pre-funded balance rather than an automatic fee. Rewards are paid from the pool for valid findings, and an unused balance can be returned if the program is closed. Partners may need to top up the pool as valid findings are paid out; underfunded programs can be paused.
Duplicate submissions generally do not require an additional payment, as the reward is normally paid only for the first valid report of a vulnerability. (Bug bounty program costs)
The financial cost is only one part of the investment. The vendor also needs to allocate engineering capacity to:
define and maintain the testing scope,
prepare test environments and documentation,
communicate with Bugcrowd and researchers,
reproduce and evaluate submitted findings,
implement and test fixes,
update dependencies or architecture where necessary, and
document the resolution.
The exact workload depends on the app’s complexity and the number and severity of reported findings. It should therefore be viewed as an ongoing engineering responsibility rather than a fixed one-time project.
A valid vulnerability report should not be understood merely as an additional cost. It is an opportunity to identify and resolve a weakness before it is discovered during a customer audit or exploited in a real customer environment.